

This article was originally published as an email newsletter from Loadsure. The views expressed here are solely those of the author and do not necessarily represent the views of FreightWaves or its affiliates.
COVID-19 added fuel to the seasonal cargo theft fire. We both know that. Did you know, however, that the pandemic is also driving a spike in ransomware?
Transportation Topics published an article about the growing ransomware threat just last month. In it, they reported that ransomware attacks have spiked 715% year-over-year — just as the data backup and security experts I know predicted.
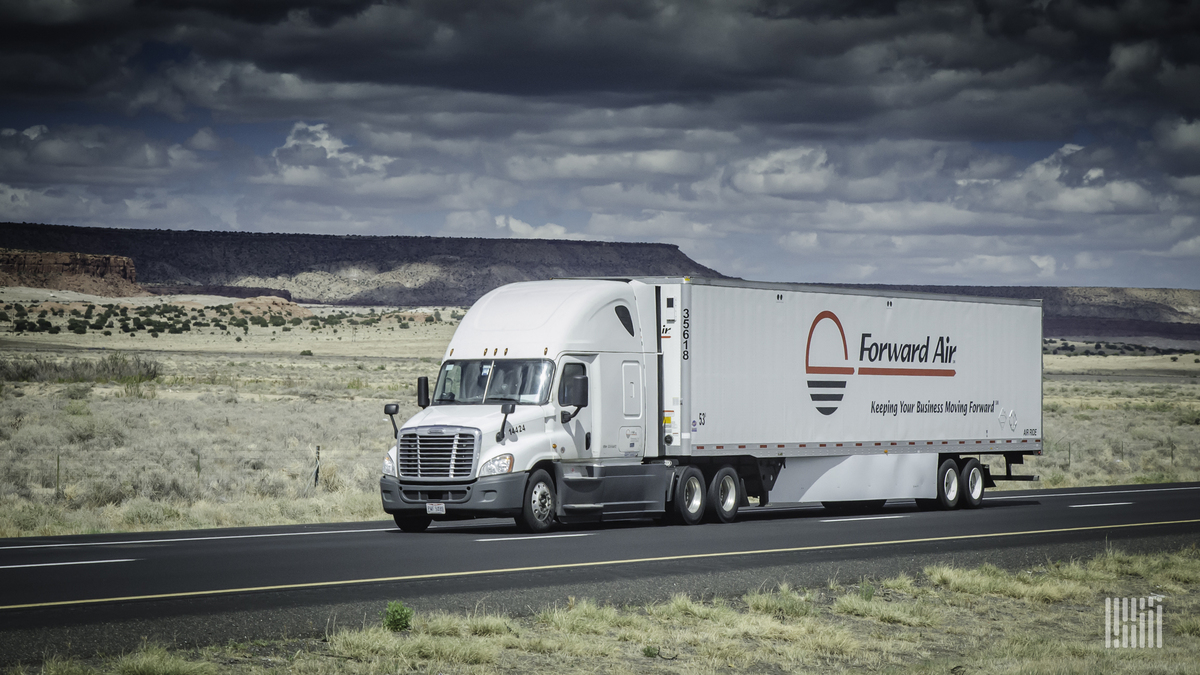
Recently, trucking and logistics company Forward Air confirmed it was one of those unlucky victims. Targeted by the Hades ransomware gang, the company was forced to pivot to manual processes in the midst of the holiday capacity crunch, disrupting business operations, delaying customer shipments and potentially impacting revenue, according to FreightWaves.
The Forward Air story is, of course, just one of many that highlight the increased risk of ransomware in the age of COVID-19. In fact, Arctic Wolf, a security operations provider to thousands of organizations and across a range of industries, has documented dozens of pandemic-related cyber threats since March alone.
And this skyrocketing cybercrime could not only bring transportation businesses, like yours, to their knees, but it could also hold devastating consequences for COVID-19 vaccine distribution.
What do we see?
Vulnerabilities and leverage points:
- Many of us are working remotely, and our data backup and security practices may not be as robust as they are at the office.
- Businesses often underfund data backup, security and disaster recovery — and transportation businesses are no exception.
- Strained by a once-in-a-100-year pandemic, we’re tired and overwhelmed — and more likely to click a link or download a file from a source that, rested and focused, might give us pause.
- There is intense pressure to rapidly distribute the COVID-19 vaccine.
And, we promise you — cybercriminals see it, too.
Worse yet, according to a New York Times article on recent attacks, “… some cybersecurity experts say they suspect something more nefarious: efforts to interfere with the distribution, or ransomware, in which the vaccines would be essentially held hostage by hackers who have gotten into the system that runs the distribution network and locked it up — and who demand a large payment to unlock it.”
Of course, your transportation business doesn’t need to play a role in COVID-19 vaccine distribution to be a target.
“Global supply chains are dependent upon information and goods exchanged through dependable and transparent methods,” says Craig Fuller, CEO of FreightWaves. “Cyberattacks put this at risk.”
Right now, we’re in the middle of a holiday capacity crunch and pressure is high. And, really, that’s all cybercriminals need — you to feel immense pressure to comply with their ransom demand.
I’ve spent years working in the data protection space, speaking with leading industry experts on ransomware protection. I wanted to ensure you were aware of the threat — and what you and leaders across your business can do about it.
How can you protect your business against the ransomware threat?
First, it’s important to understand that data security solutions cannot prevent all ransomware attacks. That’s why taking a robust, three-pronged approach to protecting your business-critical systems, applications and data is crucial.
That means investing not just in data security but end-user training and data backup and disaster recovery, as well.
Be sure to ask these questions of your company:
- Have our prime cybercrime targets — our business leaders — received ransomware training, and are they regularly communicating the importance of vigilance across the company?
- Are we regularly conducting ransomware awareness training sessions and phishing simulation testing our team? (Chris Roberts of Hillbilly Hit Squad says Wizer Training is a good option.)
- Are we immediately updating software and implementing security patches?
- Are we restricting access to systems and data to only those who absolutely need it?
- Has our IT team or managed service provider implemented a 3-2-1 backup strategy? (Do we maintain three copies of our data on two different types of media, one of which is stored offsite for disaster recovery?)
- Does our business have a ransomware crisis plan in place — and did its planning extend beyond our IT team to also include cross-department leadership, including customer service and communications?
- Does our IT team regularly test the recoverability of our systems, applications and data?
- Are we performing tabletop exercises to ensure we’re prepared — and to ensure we’ve identified any unknown vulnerabilities?
How can you avoid personally opening the door to cybercriminals?
It’s not always easy. Cybercriminals have grown increasingly sophisticated — they’re leveraging social engineering and expertly spoofing businesses we trust. And, it makes those urgent emails and web offers we receive from them nearly irresistible.
It’s why we suggest you:
- Remain suspicious of unsolicited requests for your personal data — whether you receive them by call, text or email.
- Independently verify data requests by placing a direct call to the business using the contact information on its website — never the contact information provided in the message you received.
- Don’t click links or download files from sources you don’t know and trust.
- Don’t share personal or financial data via email — and don’t click links that request this information.
- Confirm the website you’re visiting is secure before you share sensitive data (just look for the closed padlock icon and the HTTPS security protocol.)
- Look closely at email addresses and URLs for the slight spelling or punctuation changes that signal a source has been spoofed (e.g., [email protected] vs [email protected])
- Be wary of generic email greetings from people you know (if something feels off, it probably is.)
- Similarly, be vigilant of data and financial requests from folks who wouldn’t ordinarily make such requests of you, but whom you’d be inclined to immediately service (perhaps that’s your CEO or an executive-level partner you’ve never met.)
- Never use a flash drive that’s not your own or from a trusted source.
Ransomware is the quintessential example of prevention being worth a pound of cure. So, stay vigilant. We’re all in this together — and together we can keep the wheels turning.
Recent Comments