

Erica D. Borghard is a senior fellow with the New American Engagement Center at the Scowcroft Center for Strategy and Security at the Atlantic Council.
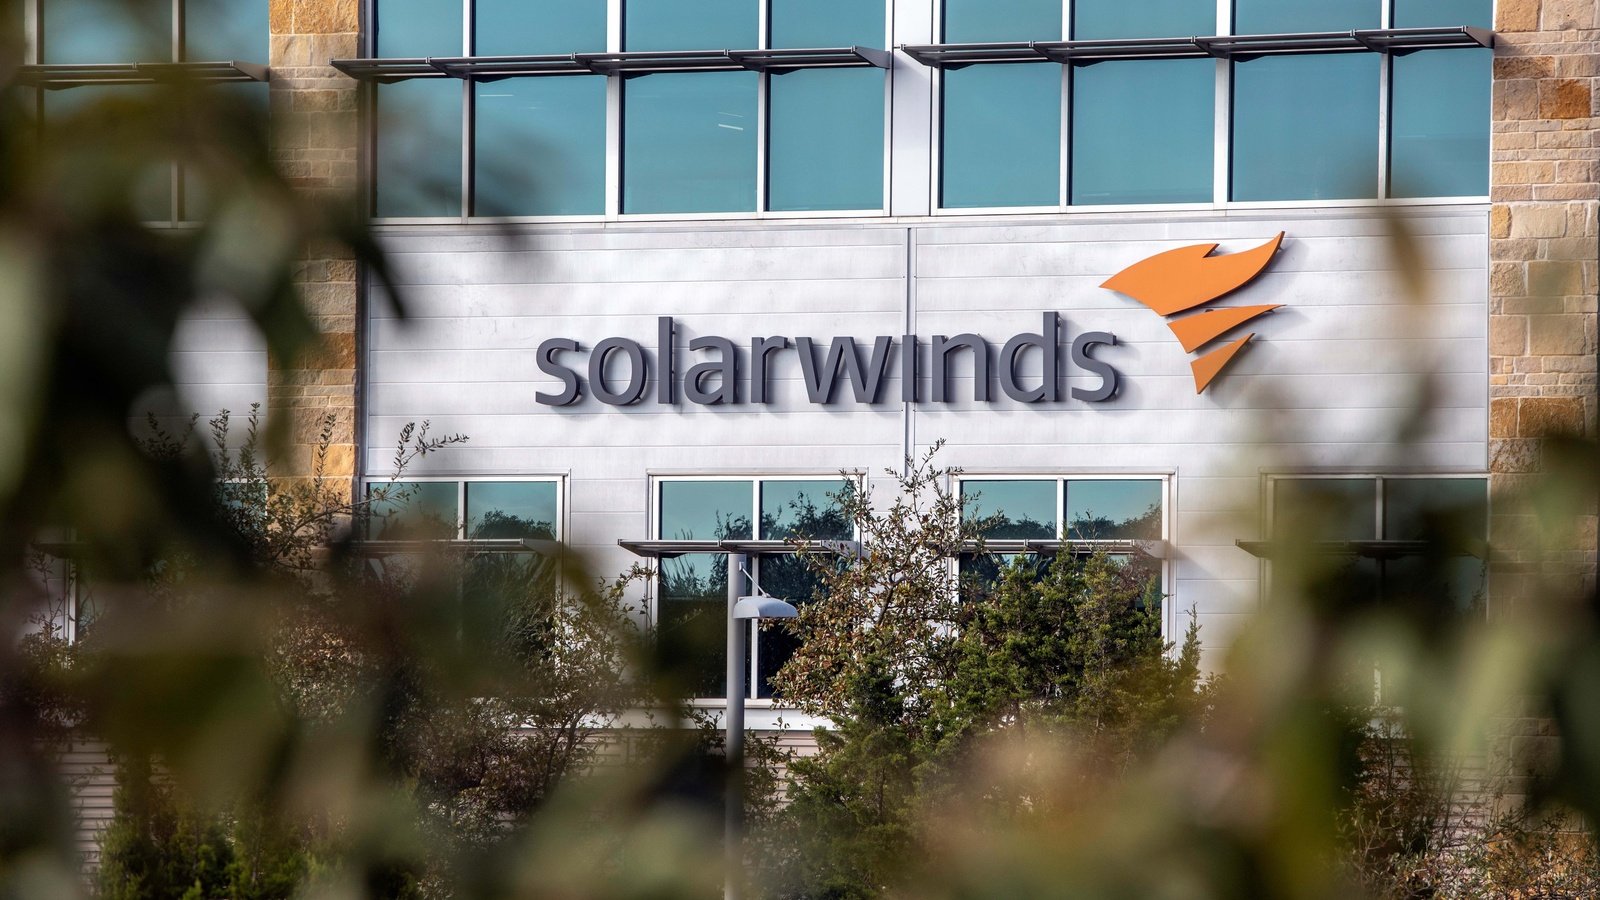
The compromise of the IT company, SolarWinds, and the breaches of multiple U.S. government agencies, including the Homeland Security, Treasury, and Commerce departments, could be the most significant cyber breach targeting the U.S. government in recent years. The extensive operation is reportedly the work of APT29 (also known as Cozy Bear), which is linked to Russian foreign intelligence. Currently, U.S. government officials are working to assess the scope of the operation, contain the damage, and ascertain the intent behind it. This incident raises two important implications for the strategic issue of the security of the supply chain for information and communications technology (ICT).
More on:
First, much of the conversation around the ICT supply chain has been dominated by the U.S.-China [PDF] rivalry and, specifically, the purported competition between Chinese and Western technology firms over their relative global market share. There is considerable hype about China’s pursuit of dominance in this arena including concerns about Made in China 2025, China Standards 2035, and China’s Military-Civil Fusion strategy. The Trump administration has enacted a number of measures aimed at curbing China’s role in the ICT supply chain, including the May 2019 Executive Order that aimed to ban Huawei and ZTE from the U.S. market. Indeed, in an interview on Monday, Secretary of State Mike Pompeo responded to a question about the SolarWinds incident by calling attention to China, rather than Russia: “We see this even more strongly from the Chinese Communist Party.”
The reality is that China is only one aspect of the challenge of supply chain security. In the case of SolarWinds—an American IT company—Russia seemingly compromised the ICT supply chain through a widely-used vendor. This incident had nothing to do with China’s position in the global supply chain. Instead, the SolarWinds case illuminates the issue of third-party risk. Third party firms, like SolarWinds, have become extraordinarily valuable, high-reward targets because they end up having a high concentration of data, access, and inroads into a number of entities. A threat actor targeting this kind of critical node in the supply chain could end up gaining access to a wide range of targets, with cascading implications.
Second, in light of the strategic significance of the ICT supply chain—the fact that nearly every aspect of modern economies and societies rests on complex global networks comprised of raw materials, hardware, and software—the United States needs a coherent and comprehensive national strategy. This was a core finding of the U.S. Cyberspace Solarium Commission. In October 2020, as a follow-on to its March 2020 report [PDF], the Commission released a white paper [PDF] on building a trusted ICT supply chain. It calls for, among other things, identifying the critical raw materials, hardware, and software the United States needs to secure, stimulating domestic investment, and working internationally to build trusted private sector partners.
Securing the ICT supply chain will be a significant undertaking, requiring large-scale investment and dedicated attention over multiple administrations. Moreover, it is nearly impossible to secure every link in the supply chain. The U.S. should therefore expect that there will continue to be critical supply chain compromises. Moreover, supply chain cybersecurity is only one element of supply chain risk. Adversaries will seek to leverage U.S. dependence on materials and technologies as bargaining chips during a crisis or as part of coercive diplomacy.
This means the ICT supply chain issue should not only be framed in terms of security, but also in terms of resilience. Resilience encompasses the ability to anticipate, withstand, rapidly restore core functions and services, and evolve as an organization in the wake of a disruptive event. A resilience-based approach assumes that some compromises and disruptions are impossible to deter or prevent and, therefore, organizations should invest in being better prepared when these instances occur.
More on:
A risk-based approach to cultivating the resilience of the ICT supply chain would include a number of elements. It would require systemically identifying and prioritizing critical assets, capabilities, functions, and dependencies. The United States needs better visibility into the supply-chain and to map dependencies across it to understand how an incursion or disruptive event in one area could have broader implications. For example, while the SolarWinds situation is still evolving, it’s not clear that the U.S. government even knows all of the departments and agencies that use SolarWinds. Prioritization should also drive decision-making around areas to invest in redundancies. A successful resilience approach would also rest on strategic intelligence capabilities to improve anticipation of and proactive response to adversary activity. This would include developing a better understanding of the threat environment, including evolving adversary intent, capabilities, and objectives; their intelligence objectives and collection requirements; and ascertaining likely avenues and methods of incursion.
As the SolarWinds incident illustrates, cultivating the security and resilience of the ICT supply chain is an enduring and vexing challenge—one that will have strategic and economic implications for decades to come.
Recent Comments